Cybersecurity & Compliance Readiness That Gets You Audit-Ready Without the Chaos
Intechgrity Solutions helps regulated businesses strengthen controls, close security gaps, prepare audit evidence, and reduce compliance risk across PCI DSS, SOC 2, HIPAA, ISO 27001, NIST, and Microsoft 365 environments.
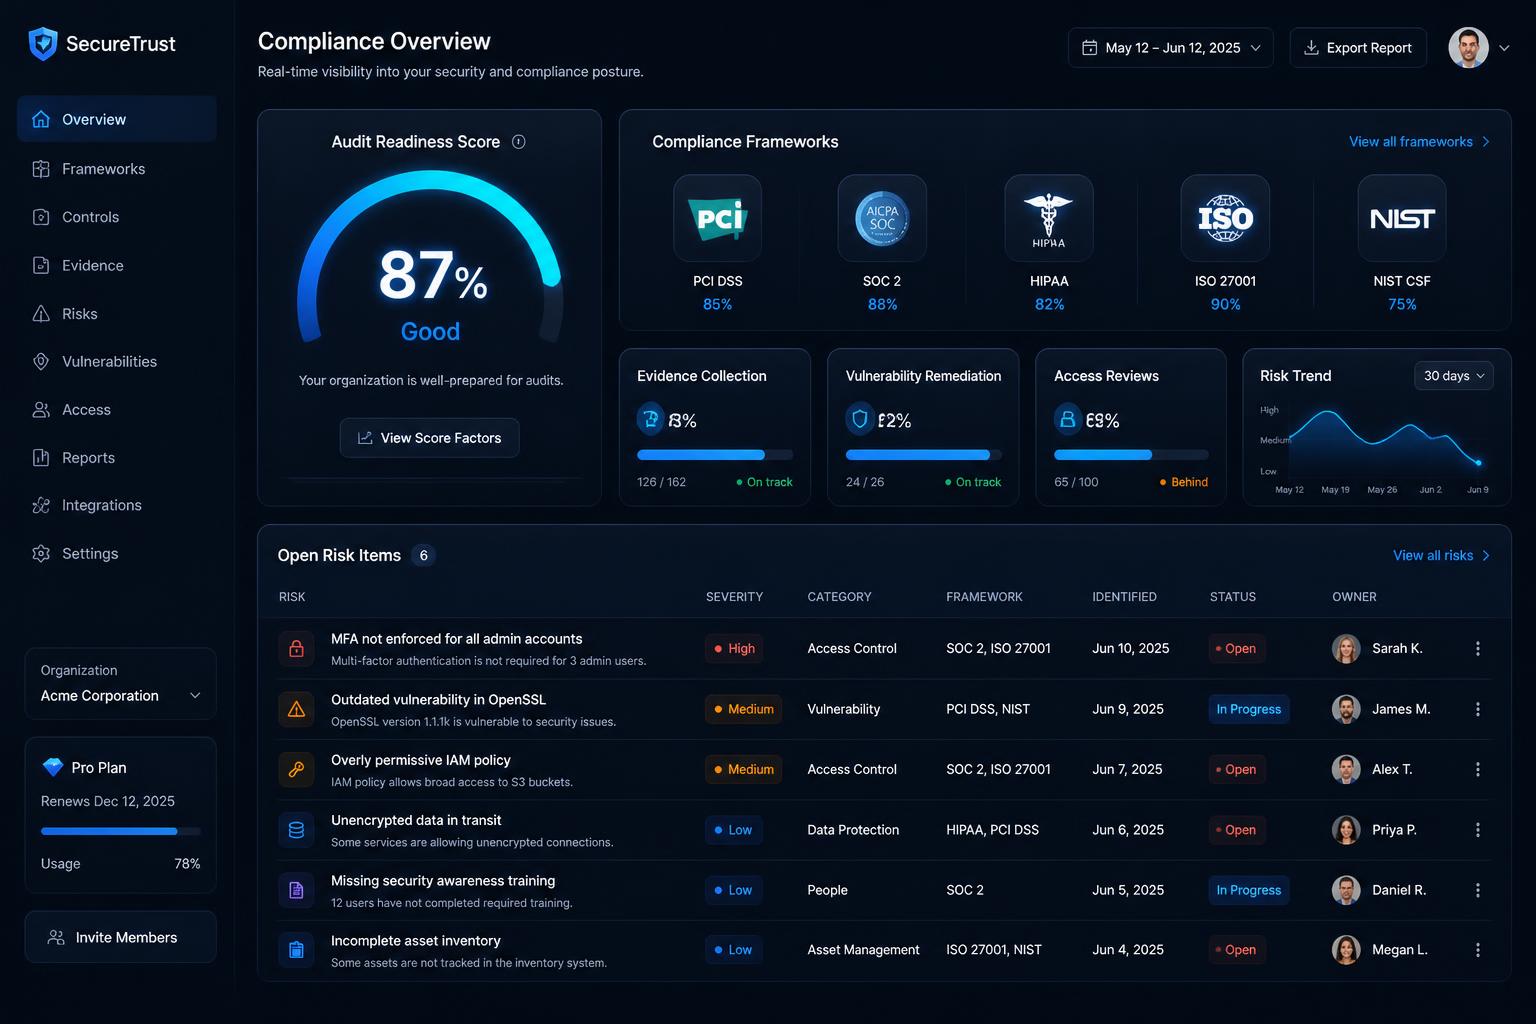
Compliance Fails When Evidence, Access, and Vulnerabilities Are Out of Control
Audit Evidence Is Scattered
Teams waste weeks chasing screenshots, tickets, approvals, policies, logs, and access records before every assessment.
Access Reviews Are Messy
Stale accounts, over-permissioned users, weak offboarding, and unclear ownership create avoidable audit findings.
Vulnerabilities Stay Open Too Long
Critical and high-risk findings need clear ownership, SLA tracking, remediation evidence, and executive visibility.
Hands-on Advisory Across the GRC Lifecycle
We work inside your environment — not from a slide deck — to strengthen controls and produce evidence assessors can actually use.
Compliance Readiness
Prepare for PCI DSS, SOC 2, HIPAA, ISO 27001, and NIST assessments with a clear roadmap and gap remediation plan.
Audit Evidence Support
Collect, organize, and validate the policies, tickets, approvals, and logs your assessors will actually request.
Identity & Access Reviews
Clean up stale accounts, over-permissioned users, and offboarding gaps across Microsoft 365 and beyond.
Vulnerability Management
Establish SLA-driven remediation, ownership, and executive reporting for critical and high-risk findings.
Policy & Control Design
Turn framework requirements into practical, operable controls that fit how your team already works.
Risk Assessments
Structured risk assessments aligned to NIST 800-30 with prioritized treatment plans your leadership can act on.
A repeatable path from gaps to audit-ready
Discover
Scoping call, framework mapping, and rapid gap assessment across your current controls and evidence.
Remediate
Prioritized cleanup: access, vulnerabilities, policies, logging, and control ownership across teams.
Prepare Evidence
Build a defensible evidence library that mirrors what assessors will request — before they ask.
Audit Support
Sit alongside your team during fieldwork, respond to auditor questions, and close findings faster.
Built for regulated and audit-driven teams
Practitioners, not slide-deck consultants
Intechgrity Solutions brings 25+ years of hands-on IT, identity, and cybersecurity operations to compliance work — from federal-scale environments to small businesses preparing for their first assessment.
Ready to reduce audit chaos?
Book a 30-minute compliance readiness call. We'll map your current state to your target framework and outline the fastest path to audit-ready.